
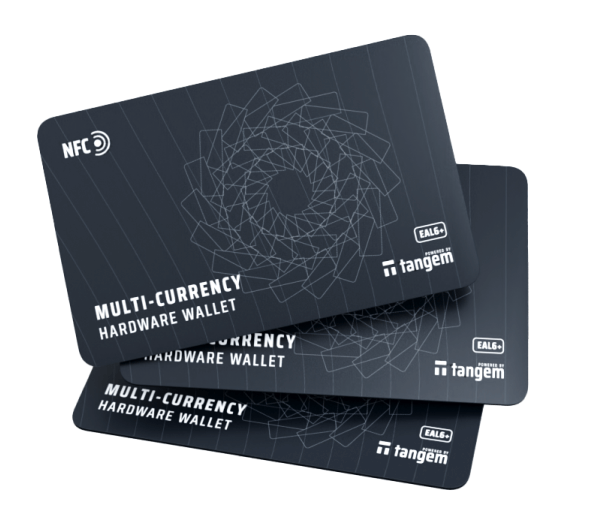
Okay, so check this out—I’ve been carrying a Tangem-style smart card in my wallet for months, and somethin’ about it still catches me off guard. Wow! It feels like a tiny piece of magic. At first I thought it would be a gimmick, but then I used it on a crowded subway platform and something clicked: security can be invisible and practical at the same time.
Here’s the thing. NFC-based crypto hardware wallets bridge two worlds. Short. They merge the simplicity of tap-to-pay with the hardened cryptography of a hardware key. Really? Yes. You use a mobile app for the UX, but the private keys never leave the NFC card. That architecture reduces attack surface dramatically, though actually—wait—it’s not a silver bullet.
My instinct said this would solve most user error. Hmm… and in many ways it does. But people still do risky stuff. On one hand the card eliminates malware risk on your phone for signing because the private key is isolated. On the other hand, social engineering and careless backups remain big threats. Initially I thought physical possession was enough, but then I remembered lost-card stories and the panic when seed phrases are mishandled.
Shortcomings matter. They’re not fatal, but they’re real. For example, NFC connectivity is not the same everywhere. Some older phones are finicky. Some cases block the signal. And until you try it a few times you feel awkward tapping your wallet to your phone like a futuristic business card exchange. (Oh, and by the way—airport security sometimes gives you a look.)
Technical bits—briefly. The card houses a secure element that signs transactions over NFC. It presents the signed transaction data back to the mobile app, which broadcasts it. Simple flow. Medium complexity under the hood. The separation is elegant because the app becomes a window, not the custodian of your keys.
Why that design matters for everyday users
Think of your current hot wallet on your phone. Fast. Convenient. But exposed. A malicious app or phishing link can coax you into approving a transaction. With an NFC card, the phone displays details but cannot move funds without the card’s signature. That changes the risk model. It turns your familiar flow into something safer, with almost no extra friction.
Check this out—I’ve linked a practical guide I trust while testing different cards and workflows: https://sites.google.com/cryptowalletuk.com/tangem-hardware-wallet/ Seriously, that resource helped me map feature differences and real-world UX. It covers compatibility quirks and recovery options that matter when you’re not at your desk.
Now let’s talk mobile apps. They do the heavy lifting for user experience—balance display, transaction composition, network selection. But they’re also the point where users make choices. Short. Good apps guide and restrict risky actions. Bad apps enable confusion. My rule of thumb: prefer apps that show transaction details clearly, and that refuse to let you sign unless the card confirms specifics. I’m biased, but details matter.
Security trade-offs deserve a clear-eyed look. You gain resilience against remote compromise. You pay with potential physical risk and device compatibility quirks. And there’s a behavioral layer—people must adopt modestly different habits. For many that’s fine. For some it’s a hurdle. On one hand I want a seamless experience. On the other hand, I’m very very protective of seed material and I accept a small learning curve.
Recovery flows are where products often fail. If you lose the card, what then? Some solutions use multi-card backups, others rely on a printed recovery code, and a few use social recovery mechanisms. None are perfect. Personally, I keep a discrete, offline backup and a trusted-person contingency. Not flashy, but it works. Your mileage will vary, and that’s okay.
Regulatory and supply considerations also pop up. NFC cards are hardware devices with firmware. Firmware updates can be a vector for improvement or, hypothetically, for supply-chain risk. Industry needs strong transparency practices—audits, open standards, and honest disclosure. The tech community is moving that way, though actually adoption of audits is uneven across vendors.
Here’s a practical checklist for anyone curious: short-term steps you can take today. First, test NFC compatibility on your phone. Short. Second, use the official mobile app and verify it on first use. Third, create a backup plan that doesn’t rely solely on the card. Fourth, practice a recovery drill once—yes, pretend you lost the card and walk through the steps. You’ll be surprised how much calmer you are afterwards.
Usability matters, too. If an experience is secure but maddening, adoption stalls. Good NFC wallets balance prompts and automation so that users don’t type in long strings but also don’t blindly approve every tap. A helpful UI shows the destination address, amount, and fee in plain language before the card signs. That combination reduces cognitive load and phishing success.
Community and ecosystem are the final piece. Standards like CTAP2 and secure element best practices help, but what actually pushes adoption is apps and services that integrate smoothly. Wallets that speak to exchanges, DeFi apps, and payment rails with clear signing flows win users. Developers need to build for people—not just for cryptographers. That seems obvious, but it gets missed.
FAQ
Is an NFC smart card safer than a hardware USB wallet?
Short answer: often yes for mobile-first users. NFC cards reduce the attack surface by keeping keys off your phone and off PCs, which are more commonly targeted. Long answer: security depends on threat model. If you’re protecting vast sums, multiple layers (multi-sig, air-gapped signing, cold-storage) might be preferable. But for everyday use and portability, NFC cards offer a strong balance of security and convenience.
What happens if I lose the card?
It depends on your backup strategy. If you used a recovery seed, you can restore to a new card or a different wallet; if you used a non-exportable key tied to a vendor’s issuance, follow their recovery instructions. Practice recovery so you’re not inventing it under stress. Also: consider splitting backups and keeping them in separate secure locations.
I’ll be honest—I’m excited but cautious. The tech feels like a real step forward for everyday crypto security, yet the ecosystem still needs polish. Some parts bug me, like inconsistent apps and fuzzy recovery guides. But when it works, it simplifies the trade-off between safety and usability in a way that makes sense for normal people. That’s the real win.